
Gartner published two forecasts a year ago that still frame this market. In August 2025, the firm predicted 40% of enterprise applications would integrate task-specific AI agents by the end of 2026, up from less than 5%. Two months earlier, it warned that over 40% of agentic AI projects will be canceled by the end of 2027 because of escalating costs, unclear business value, or inadequate risk controls.
Read the scope carefully. Both figures describe enterprise software, not government. Plenty of articles quote them as public-sector statistics anyway.
Analyst Anushree Verma blames much of the failure rate on agent washing: vendors rebranding assistants, RPA and chatbots as agentic. Gartner estimates only about 130 out of thousands of such vendors are real.
Government numbers carry the same caveat. IDC research for Salesforce found 82% of surveyed government organizations had already adopted AI agents, but the sample covered 118 U.S. leaders and the vendor paid for it. The line buried in the same research matters more: IDC found that while many agencies are implementing agent-driven workflows, few have moved beyond pilots.
So this guide asks a narrower question than most. Not whether government should adopt agentic AI, but which workflows are ready to delegate — and how to tell a working system from a press release.
What Counts as Agentic

A chatbot answers. An agent acts.
Picture someone applying for a business license. A chatbot lists the documents. An agent checks eligibility against live records, pre-fills the form, flags gaps, and routes the file to a caseworker. Nobody scripted that sequence, and the agent holds the goal across a multi-day approval instead of restarting each time the case reopens.
Ottawa draws the same line. Treasury Board guidance defines an AI agent as a system that perceives and acts on its environment to achieve a goal, and agentic AI as coordinated agents pursuing goals on a user’s behalf.
| Capability | RPA | Generative AI | Agentic AI |
|---|---|---|---|
| Follows fixed rules | Yes | No | No |
| Creates new content | No | Yes | Yes |
| Plans multi-step tasks | No | Limited | Yes |
| Selects its own tools | No | No | Yes |
| Adapts mid-task | No | No | Yes |
| Retains goal state | No | No | Yes |
Definitions collapse during a demo, so carry a checklist instead. A system is meaningfully agentic when it takes an objective rather than a fixed sequence, revises its own intermediate steps, selects among authorized tools, reacts to information that changes mid-task, holds state across sessions, executes permitted actions rather than only recommending them, and escalates when confidence or authority runs out.
Script every branch and let the model fill in text, and you have automation wearing a label. Ask each vendor to run an unscripted case in front of you. Real agents reason through it and flag uncertainty. Rebranded ones guess.
Where Governments Are Testing and Deploying
Documented examples span executive orders, cabinet targets, live platforms, and supplier announcements. They differ in maturity, and that difference is the story.
| Government | System | Status |
|---|---|---|
| Virginia | EO 51 regulatory review | Executive order |
| UAE (federal) | Agentic AI framework | Cabinet-approved target |
| Abu Dhabi | TAMM AutoGov | Launched platform feature |
| Estonia | Bürokratt | Moving toward agent network |
| Vail, CO | HPE smart city platform | Supplier announcement |
| Lancaster, CA | Labyrinth permitting | Supplier announcement |
Virginia
Governor Youngkin signed Executive Order 51 on 11 July 2025, launching a first-of-its-kind agentic AI regulatory reduction pilot. The state’s Office of Regulatory Management described Virginia as the first to use an agentic tool for regulatory reduction. It scans regulations and guidance, flags where a rule contradicts its statute, identifies redundancies, and highlights language to simplify.
The durable part comes after the pilot. EO 51 requires agencies to use AI in their four-year periodic reviews, applying to everything after 31 December, with humans and tools both playing a role.
One correction worth making loudly. Virginia’s headline figures — roughly 26.8% of requirements streamlined, 47.9% of guidance words cut — measure the 2022 reduction effort that preceded the tool. Agencies had already beaten the 25% target before EO 51 existed. An April 2026 case study notes the AI work ran in the administration’s final months, making its results hard to separate from the broader program. Versions circulating as “35%” and “50%” match no published figure at all.
UAE and Abu Dhabi
The UAE Cabinet approved a framework on 23 April 2026 to convert half of government sectors, services and operations to autonomous models within two years, with a task force chaired by Cabinet Affairs Minister Mohammad Al Gergawi. An ambition with institutional weight, not a deployment.
Abu Dhabi is further along. Its Department of Government Enablement launched TAMM AutoGov at GITEX in October 2025, billing it as an AI public servant that handles license renewals, bill payments and healthcare appointments without users logging in or tracking deadlines, inside a platform carrying more than 1,100 services.
The governance detail deserves copying: users set their own automation level per service. Citizens choose their own autonomy tier.
One caution. A live platform doesn’t prove every feature inside it runs unattended. How much of AutoGov executes without a human, per transaction type, isn’t something public sources settle.
Estonia’s Bürokratt sits earlier — a virtual assistant across public institutions, now moving toward a network where institutional agents talk to each other.
Vail and Lancaster: Check the Tense
Both municipal examples come from supplier announcements, and both read in future tense a year later.
Vail will adopt HPE’s agentic smart city platform, running it on the town’s own solar- and wind-powered data center, and will use it for public safety, emergency response, wildfire detection, traffic and permitting, according to an announcement HPE made in October 2025. Integration partner SHI still described Vail as the town that will be first to deploy it as late as March 2026.
Lancaster plans to use agentic workflows to pre-screen permit applications, validate requirements, and flag missing components, under a co-designed partnership with Labrynth announced in September 2025.
Both are worth watching. Neither has published outcome data. A 4,300-resident town and a mid-size California city are running plans, not proofs.
AI Agents Are Expanding the Attack Surface
Alert triage and incident response make sense on paper. Public evidence of autonomous agents inside U.S. agency security operations does not exist in volume.
The sharper issue is that agents on your network are participants in it. Singapore recommends threat modelling for memory poisoning, tool misuse, and privilege compromise. Indirect prompt injection through untrusted inputs — a resident-submitted PDF, a scraped record — and goal hijacking are agent-native attack surfaces, and legacy tooling catches neither. Anyone unconvinced that agents find unintended uses quickly should read what happened when agents were turned loose on open platforms earlier this year.
How an Agent Reaches a Legacy System
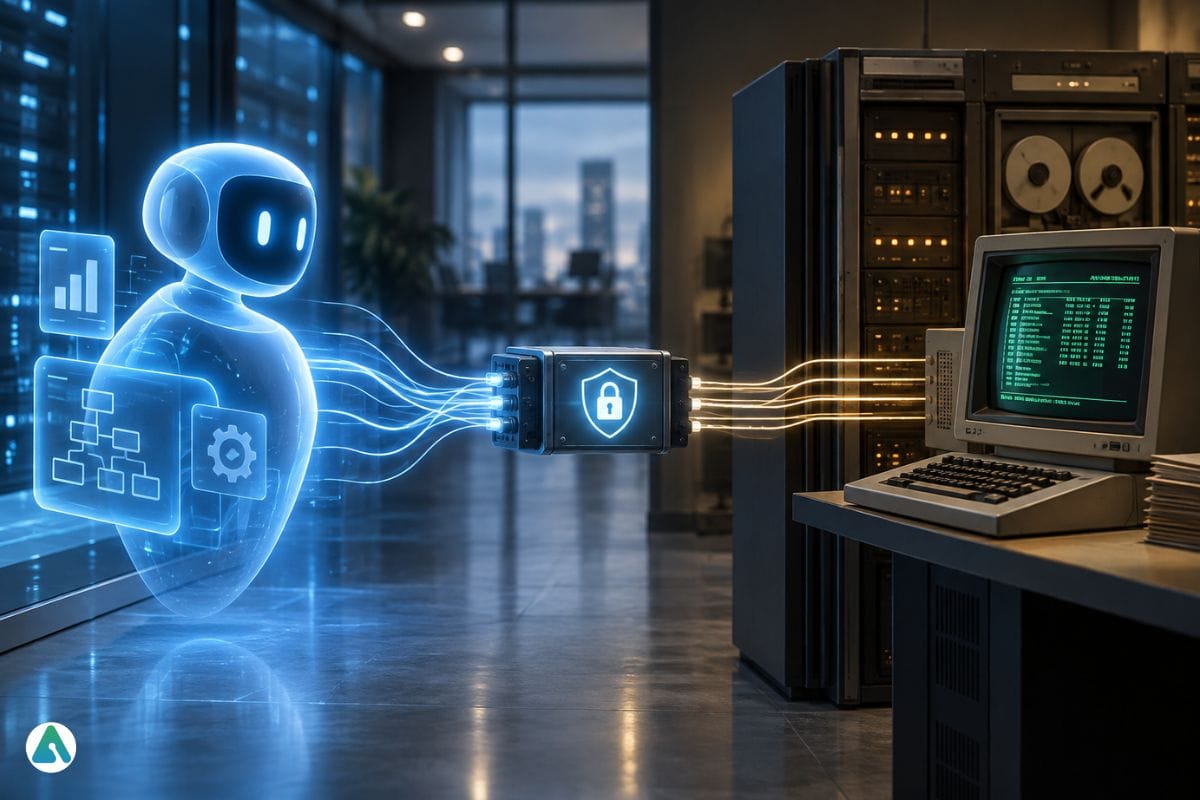

Vendors answer the integration question with a protocol name. Architects need the layer below it.
Standards like Model Context Protocol and Agent-to-Agent are emerging as connective tissue for tool access and handoffs. A protocol existing and an agency running it against a mainframe remain different facts.
For systems with no modern API — COBOL batch jobs, AS/400 green screens, a permitting database whose vendor folded — the chain that preserves least privilege runs:
Agent → MCP server → service layer → scoped service account → legacy system
Four rules make it defensible. The MCP server holds credentials, never the agent, which sees only a named tool like check_zoning_status(parcel_id). Each tool maps to one operation with one permission, so read and write use separate accounts, and a read agent physically cannot write. The service layer logs which agent called which tool under whose authority, because database logs won’t tell you that. And screen-scraping bridges count as write access — a robot driving a terminal session carries a human’s permissions, so scope it down or don’t build it.
Ask how the agent reaches your systems before asking what it can do.
Governance: Autonomy You Can Undo
The independence that makes agents useful makes them dangerous when scoped badly. An agent that acts can act on bad data at speed.
AWS’s public-sector guidance gives risk boards a four-tier model: Scope 1 is read-only and changes nothing; Scope 2 proposes actions a human approves individually; Scope 3 executes on its own once a human starts the task, with monitoring instead of per-action sign-off; Scope 4 initiates and executes independently.
Controls should tighten as an agent’s power to initiate, modify, and cross trust boundaries grows. Current guidance agrees. Ottawa’s guide on agentic AI states that agentic systems work best in tightly scoped internal workflows with clear boundaries and limited permissions, with accountable public servants authorizing consequential actions.
Design for Reversal
Most governance writing asks whether an agent may act. Ask instead what happens after it acts wrongly.
You need pause, rollback, reversal, dispute and escalation paths — not just logs. This bites when an agent updates a record, issues a notice, or fires a downstream workflow another system already consumed.
Singapore built this in when IMDA launched its agentic framework at Davos in January 2026, treating reversibility as a factor that sets an agent’s risk level alongside tolerance for error, data sensitivity, and task complexity, and recommending offline mechanisms for malfunctions.
Define who approves. Then define how you recover when the approval was wrong.
Permissions and Oversight
Give an agent only what its task needs. Singapore recommends limiting access to the minimum required tools and data, defining standard operating procedures, and giving each agent a unique identity tied to a supervising person. Ottawa makes limited permissions central to its scoping advice.
This control is the most repeated across current frameworks and the first abandoned under delivery pressure. Engineering teams already know what happens when permission checks get switched off for speed in a coding workflow; the same shortcut in a benefits system produces a different class of incident.
A human checkpoint works only if the human checks. Under caseload pressure, people defer to the machine, and a caseworker clearing fifty flagged files a day provides cover rather than oversight. Singapore’s May 2026 update added guidance specifically on guarding against that bias. Three practical additions of our own: sample a random slice for deep audit, rotate who reviews high-stakes flags, and track approval rates per reviewer so a perfect record surfaces as a warning.
Finally, make decision records readable by people, not just developers. If an agent denies an application, someone must be able to see why without querying a log store.
Procurement and Real Cost
For agencies moving from AI experimentation to real deployment, outside expertise can help bridge the gap between technical ambition and operational reality. The challenge is knowing which capabilities to build in-house and which to bring in through a trusted partner. That balance reflects a broader shift in how businesses approach external expertise, as discussed in Why Agencies Are Outsourcing Expertise, Not Strategy.
Cost It Before You Scope It
Total cost is not the license fee and not just tokens:
Annual cost ≈ (transactions × steps × tokens per step × price per token) + orchestration + retrieval + monitoring + integration build + human review hours + evaluation + incident response
Work an example. A permit-screening agent handling 20,000 applications a year at 8 reasoning steps and 4,000 tokens per step burns 640 million tokens before retries, retrieval, or the evaluation runs you’ll repeat every time a model updates.
Two lines budget offices miss. Retries and tool-call loops typically add 30–60% over the happy path. And review time rarely reaches zero at Scope 2, so budget the caseworker minutes — that figure often exceeds inference cost.
Ask for cost-per-transaction at your real volume. Price the exit if the orchestration layer is proprietary. Then pin down what the contract actually guarantees: which security authorizations exist today for which environment, whether the autonomy boundary is configurable by you, whether audit output is human-readable, and how an executed action gets reversed.
The 7-Gate Readiness Test

Stop asking whether your agency should adopt agentic AI. Ask whether this workflow is ready to delegate. Every gate is pass or fail, and a failure means fix the gate, not proceed carefully.
- Use case. Narrow, high-volume, and low-consequence enough that an early error is recoverable? Benefits eligibility and enforcement fail here.
- Authority. Can the agency lawfully delegate this action, under which statute?
- Data. Are the records unified, current, and queryable before you build? Fragmented source data kills more pilots than weak models.
- Permissions. Scoped to this task, with a distinct identity for the agent? Broad access granted to save time is the fastest route from productivity win to incident.
- Checkpoint. Which actions need sign-off, and how will you catch rubber-stamping?
- Recovery. Can you pause, reverse, and remediate after execution, downstream effects included?
- Evidence. Will a human-readable decision record exist from day one? If nobody owns what the agent does, nobody owns it at exactly the wrong moment.
What Comes Next
Governance is hardening from voluntary guidance into binding expectation, and federal high-impact practices now carry a discontinuation consequence. More municipal platforms will follow Vail’s model, and some will finally publish the outcome data this category lacks. The UAE’s two-year target becomes the field’s natural experiment: hit it, and the cautious Scope 1–2 posture most Western agencies hold will face real pressure; miss it, and that’s the most useful data point anyone gets.
One honest objection to all of this. Caution isn’t the only force acting on agencies. Elected officials face pressure to show modernization inside an electoral cycle, and a signed contract is a visible deliverable long before any workflow improves. Gartner’s forecast describes what happens to projects, not to procurement. Agencies will keep buying whether or not the last cohort scaled — which is exactly why the gates matter. Politics decides whether you buy. Governance decides whether you survive what you bought.
Agentic AI in government has left the theoretical stage without reaching maturity. Virginia rests on an executive order, Abu Dhabi runs a live platform, Vail and Lancaster remain announcements, and the UAE has a target with a task force. The agencies that capture value won’t be the fastest. They’ll be the ones pairing autonomy with clean data, scoped access, real oversight, and a working reverse gear.
FAQs
Q. How does agentic AI differ from RPA and generative AI?
RPA follows fixed scripts and breaks when the process changes. Generative AI responds to a prompt and resets. Agentic AI takes an objective, sequences its own steps, and carries state.
Q. Which governments are actually using it?
Virginia, Abu Dhabi, Estonia, and the UAE at the federal level, plus announced municipal projects in Vail and Lancaster. Maturity varies sharply — see the status table above.
Q. How do I spot a vendor who isn’t really selling agentic AI?
Demand a live unscripted case. Gartner puts genuinely agentic vendors at roughly 130 out of thousands.
Q. What are the biggest risks?
Fragmented data, over-broad access, unreadable audit trails, rubber-stamped oversight, prompt injection and memory poisoning, and cancellation from underestimated integration cost.
Q. Can agencies use commercial AI agents?
Yes, with authorization. Federal cloud may require FedRAMP or equivalent; state rules vary. Federal agencies also work under OMB M-25-21 and M-25-22. Data residency, access controls and auditability decide the rest.
Related: 11 Best Agentic AI Frameworks in 2026: A Complete Decision Guide
| Disclaimer: Government AI is evolving fast, and deployments, policies, and capabilities can change. This article is for informational purposes only—always verify current agency guidance, regulations, and security requirements before acting on it. |
